

Don't Take the Bait
Friday, October 2, 2026
Story By: OSU Agriculture IT | dasnr_it@okstate.edu
Protect yourself and others from phishing with the Core 4 and the SLAM Method.
What is Phishing?
Phishing is a cyberattack that uses deceptive email, text messages, calls, or websites to trick people into revealing passwords, sensitive information, sending money, or opening harmful content.
Phishing can look familiar.
A phishing message may appear to come from a coworker, bank, delivery service, vendor, or even the IT department. The scammer's goal is to make you react quickly (and most of the time out of fear) before you stop to verify the request.
Common Warning Signs
- An unexpected request involving passwords, payments, gift cards, or sensitive information
- Urgent language, threats, or pressure to act immediately
- A sender address or website that is misspelled, masked, or slightly altered
- A link or attachment you were not expecting
- A message that does not sound like the person or organization it claims to represent
Pause before you act
Urgency is a scammer’s strongest tool. Take a moment to check the sender, inspect the link, question the attachment, and read the full message.
The Core 4 of Phishing Prevention
Four everyday habits can make stolen credentials and deceptive messages much less effective.
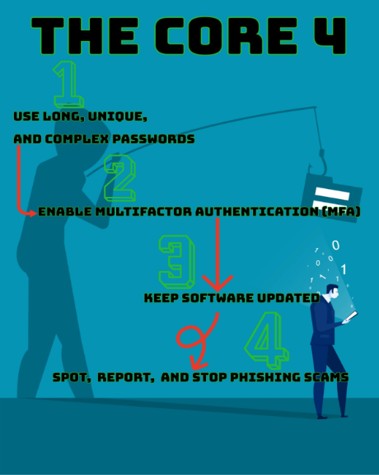
- Use long, unique passwords
Use a different password for every account. Longer passphrases are easier to remember and harder to guess. A trusted password manager such as Google Password Manager can help create and store unique credentials. - Enable multifactor authentication
MFA adds a second verification step. Even if a password is stolen, that extra check can prevent unauthorized access. Never approve an MFA prompt you did not initiate. - Keep software updated
Updates often include important security fixes. Install operating system, browser, and application updates promptly, and enable automatic updates. - Spot, report, and stop phishing
Do not click, reply, or open unexpected attachments. Report the message to IT or abuse.okstate.edu so others can be protected.
Use the SLAM Method
When an email looks unusual, SLAM gives you a quick, repeatable way to inspect it before acting.
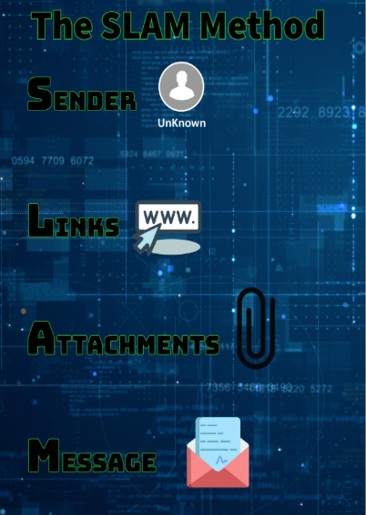
S- Sender
Check the full email address, not only the display name. Ask whether you recognize the sender and whether the request fits the normal relationship.
L- Links
Hover over a link before selecting it. Look for misspellings, misleading domains, shortened addresses, or destinations that do not match the message.
A- Attachments
Ask whether you expected the file and whether the file type makes sense. If you are unsure, verify with the sender using a known phone number or new message.
M- Message
Watch for pressure, secrecy, threats, unusual wording, broad wording (such as user or customer), or payment request.
See Something Suspicious? Report It.
Scam prevention is a team effort. Whenever you report a suspicious message or link, it could protect your team and others from falling a victim to the same message or link.
Stop. Do not click, reply or open.
Report any suspicious behavior to an IT representative
What To Do
- Report it as soon as possible.
- If you already clicked, opened a file, entered a password, or approved an MFA request, contact IT immediately.
- Delete the message only after it has been reported, and you are instructed that it is safe to do so
When in doubt, report it.
It is better to report a legitimate message by mistake than to ignore a real phishing attempt. You are not expected to investigate the message yourself.
The next phishing attempt could arrive at any time, but a few moments of caution can make all the difference. Remember the Core 4, use the SLAM Method when something feels off, and if you receive a message that seems unusual or unexpected, do not hesitate to report it. By working together, we can help make our organization, clubs, and classrooms safer and more secure for everyone.
For more information, visit our website.